mikrotik: failover gateway
Translation of the original in Catalan. Read it in: CatalàCastellano
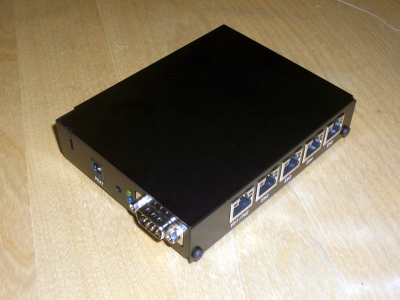
Today I've refreshed my memory a bit, it's been a month or two since I last played with mikrotiks. Well then, for a client I had to set up a failover gateway and since you already know that I'm a declared fan of mikrotiks to do this I've used an RB150. In case this sounds like Chinese to you, I'm sure that with a small explanation you'll find it very useful. Well then, more and more companies have two internet connections and what they want is that when either of the two connections goes down the other connection takes over all the traffic without having to touch anything.
Obviously to do this what we need is an element in charge of redirecting all the traffic to one router or the other depending on whether the internet connection is failing or not. The solution I propose is very simple and can be improved enormously. For example, the only thing I'll explain is using one of the two routers and when it fails sending the traffic to the other, but it isn't very difficult to create some policy routes to balance traffic between the two routers while they are operational. But to avoid complicating things I'll stick to the basic example. From here on, the foundation will be more than ready for you to do cooler things.
scenario
The RB150 will have the LAN network on ethernet 1. On ethernet 4 the WAN1 and on ethernet 5 the WAN2. Both interfaces have the ADSL router in monopuesto. That is, I have the public IP on the router's interface.
how it works
By default, we'll go out through WAN1 and when it fails we'll go out through WAN2.
configuration
I assume the basic configurations are already done, that is, IP assignment to interfaces and the masquerading of internal IPs towards internet. That I suppose has no difficulty at all, if anyone needs help just let me know.
We create two scripts to be launched when the connection via WAN1 has to be launched and the other via WAN2:
Script for WAN1:
:log info wan_1
/ip route set [/ip route find dst-address="0.0.0.0/0"] gateway=IP_GW_WAN1
Script for WAN2:
:log info wan_2
/ip route set [/ip route find dst-address="0.0.0.0/0"] gateway=IP_GW_WAN2
If we're interested in each of the scripts we can add whatever is needed. In case you're not used to working with scripts on the mikrotik you have to put them in /system scripts. There add two entries and that's it. As always this will be much more comfortable to do from the winbox than from the cli.
Now we only need to create an entry in the netwatch tool, this is done in /tool netwatch. To the entry we'll tell it to ping every interval of time we decide and to have a fixed timeout and if the pings don't come back then the indicated script will be run. Basically the netwatch entries have two states, up and down, and we can associate a script to be launched in case there is an oscillation towards one of the two states. This is done like this:
add host=208.67.222.222 timeout=10s interval=1m up-script=wan1 down-script=wan2 \
comment="Failover Gateway Script" disabled=no
What we do is check whether we reach one of the OpenDNS servers every 1minute and we wait at most 10s for the ping to come back. Then notice how we associate each of the scripts we programmed before to the states of this test.
As you can see this is quite simple, the trick is that you play with ECMP and policy routing and turn the RB150 into a full load balancer with line failure support. It is also very simple for you to balance the internet incoming traffic towards one ADSL or the other, to do this I recommend you play with the DDNS that you can update through the scripts mentioned, you only need to launch the request to update the IP associated with the DDNS and the remote users will come in through one line or the other.
3 comments
Comments from the old blog, as they were written. Comments are closed.
toolbattery
good read
laptopbattery
Thank you for this outstanding article
battery
Thank you for this outstanding article.