Wikid - Authentication server
Translation of the original in Catalan. Read it in: CatalàCastellano
Before starting, let me make it clear that this is a product with a dual licence, with some differences between the paid licence and the free one. That said, both product variants are open source, although the paid one includes some component which, I would say, does not have its source code released, such as the Radius server programmed in Java.
Wikid is a two-factor authentication server. This means that it combines two authentication systems. In this case asymmetric authentication based on a public key plus a one-time password (OTP). In this way a level of security equivalent to that of hardware-based tokens is achieved, but with all the flexibility and the benefits of software. Thanks to this software component the OTP system can work on all kinds of clients: Blackberries, phones, Palms, PocketPCs, Windows, Linux and Mac.
If you are not very familiar with these authentication systems you can take a look at the following diagram, which I find very explanatory.
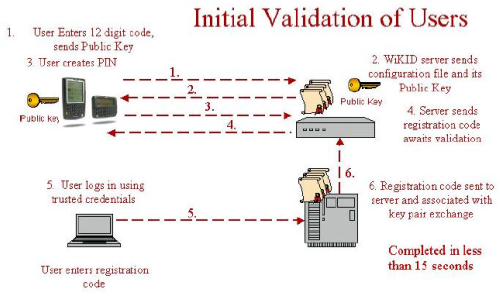
An even more detailed but also more generic diagram would be this one. As can be seen in both diagrams, the level of security achieved with this authentication can be considered very high and it is also very simple to use for the end user. Let's summarize from the point of view of the system user. When this user, for example, wants to connect to a secure website, VPN, FTP, WebDAV, mail, etc., the first thing to do is open the Wikid software client and request the OTP key. Then he connects in a completely conventional way to the service he wanted to access and this, as always, asks him for authentication and then the client enters his temporary key (OTP). This is very good because when someone asks us for the key to access somewhere we can tell them with all certainty: I don't know my key. If we still want to give them the key we can generate it and give it to them with the certainty that they will not be able to use it again. Often the software client that will give us the OTP key asks us for a PIN code to access it. This is the only key we will have to remember.
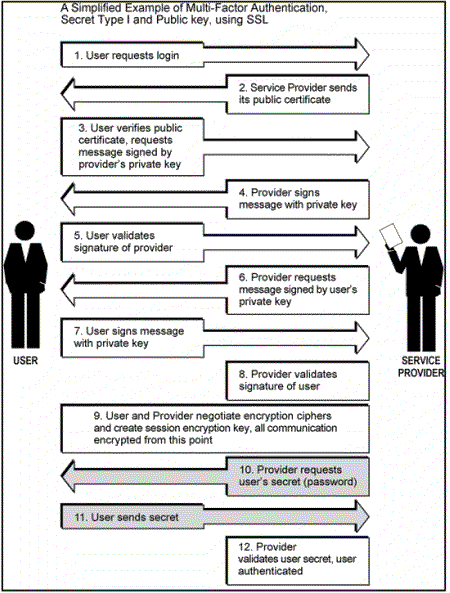
The system basically consists of three parts: the Wikid server, the Wikid client and the network service (network service or wikid network client). The latter is the service for which we want it to use the Wikid authentication system. For example, PAM, SSH, FTP, OpenVPN, IMAP server, a website programmed in PHP, Ruby, etc. So, we configure the service properly so that when it is time to authenticate it goes to look for authentication on the Wikid server, and our network service then automatically supports authentication via certificates and temporary keys. That is, the authentication system is already considered high security.
If instead of using a temporary key we want to use a biometric system, a SmartCard, a token hardware, etc., we can do that too. In this way we can make the client authenticate completely automatically without asking us for any key. Nevertheless, access to the biometric system, SmartCard, etc. is usually protected with a PIN code in order to ensure that the physical access to the device is legitimate.
The product's own website has several help videos and quite a few howtos. But if we want more detailed information, my recommendation is that you go to HowtoForge and type "wikid" in its search engine and a good bunch of manuals on how to configure Wikid as an authentication server will come up. For example, OpenVPN, SSH, FreeNX, WebDAV, etc.
5 comments
Comments from the old blog, as they were written. Comments are closed.
Javier Mart
Muy buena Review, me la apunto para probarlo!.
Gracias.
brainstorm
Només un detall de taliban :P .... El link cap a wikid hauria de tenir les "www" ;)
—
[2]
No sabia que era tan vital això de les 'www' de fet, jo no les acostumo a posar mai a menys que el servidor doni algún problema i m'obligui a posar-les.
Nick
Thanks for the review (I think :).
It looks like we have a problem with our webserver routing. You might try http://www.wikidsystems.com until we get it fixed.
Nick
—
Ja he modificat la URL. Tot i que com comenten la gent de Wikid no hauria de passar l'error que tenen.
Per això no entenc el que em deian en BrainStorm sobre ser talivan...
Apa resolt i llestos!